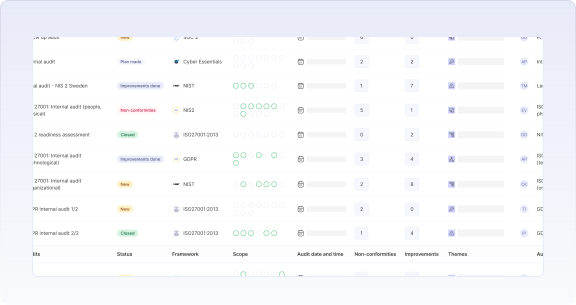
Service: ISO internal audit - your own interna auditor
Dunamis Assure - internal audit that truly strengthens governance
Get an independent assessment of whether your management systems for quality, environmental management, information security, and AI are functioning as intended. We audit ISO 9001, ISO 14001, ISO 27001, and ISO 42001 using the same methodological rigor as accredited certification bodies.
An audit should not be an exam, but a quality assurance process. We audit to help you improve. Not to point out mistakes.
A documented system is not the same as a system that works
Many organizations are required to conduct internal audits but lack the time, resources, or sufficient internal independence to do so effectively. The result is often a compliance exercise that adds little value to management and governance. That’s where we come in.
Independence and objectivity
An external auditor is free from bias and conflicts of interest. This provides management with an objective assessment of how the management system actually works in practice, rather than merely checking the documentation.
Ready for an external audit
We identify nonconformities and areas for improvement before the certification body arrives. This gives you time to address findings, resolve nonconformities, and approach the external audit with confidence.
Better decision-making insights
A professional audit reveals the maturity of an organization's quality, environmental, information security, and AI management practices. It provides management with a solid foundation for prioritizing the right actions based on risk rather than gut feeling.
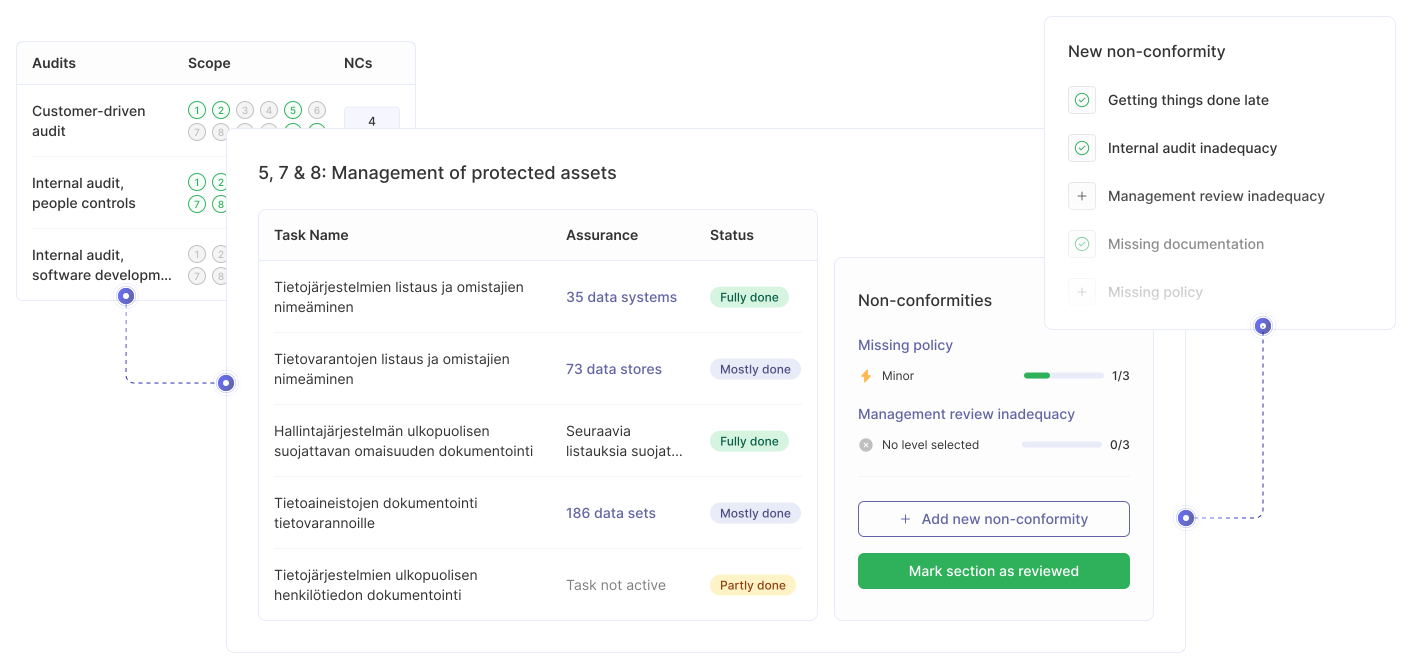
THIS IS WHAT YOU GET
Identify the findings before the external auditor does
An internal audit can be a box-ticking exercise or a valuable management tool. With us, it’s the latter: you gain a clear understanding of what actually works and what needs to be improved, well in advance.
Independent view on what should work
1
Integrated management system
Internal audit against ISO 27001, ISO 9001, and integrated management systems. We check that the system is actually followed, not just that it is documented.
2
Risk management and internal control
Assessment of whether risk management is real and updated, and whether internal control captures what it should.
3
Compliance and regulatory requirements
Audit against the requirements that apply to you, NIS2, DORA, the Digital Security Act, and industry-specific requirements.
4
Preparation for external audit
We conduct the internal audit before the certification body arrives, close findings, and prepare you for step 1 and step 2.
Internal audit is a requirement, and an opportunity
For an independent assessment, the auditor should not be the one who built the system. Therefore, Assure is a natural complement to Dunamis Comply:
Comply establishes and operates the management system.
Assure provides the independent view.